How to Convert HTTP to HTTPS: The Comprehensive Guide
Updated on |By QPSoftware
How to convert HTTP to HTTPS, in short: install an SSL/TLS certificate on your server (Let’s Encrypt issues them for free), update internal links and resources to https, redirect every HTTP URL to its HTTPS version with a 301 redirect, then update your sitemap, canonical tags and Search Console. Test everything before switching the live site.
Key takeaways
- Google announced in February 2018 that Chrome 68 would mark all HTTP sites as “not secure”, and in 2014 that HTTPS would be a ranking signal.
- Let’s Encrypt provides free certificates; paid certificates add organization or extended validation.
- Update hard-coded links, scripts and CDN settings to avoid mixed content warnings.
- Use server-side 301 redirects, then update robots.txt, sitemaps, canonical tags and hreflang.
- Add the HTTPS property in Search Console, submit the new sitemap, and update analytics, ads and email tools.
In February 2018, Google announced that Chrome would mark all HTTP sites as “not secure”, starting with Chrome 68 in July 2018. Four years earlier, in 2014, Google had announced that it would use HTTPS as a ranking signal, a very lightweight one at the time.
HTTPS is a more secure way to browse, so migrating remains worthwhile for every website. Follow this guide if your site has not moved to HTTPS yet. If your site is live and cannot afford downtime, plan the migration as part of your ongoing website maintenance.
This guide was first published in 2019. Where tools have changed since, the steps below say so; interfaces keep evolving, so check each provider’s current documentation.
1. Get an SSL Certificate
An SSL certificate binds a cryptographic key to the details of an organization or a website. Once installed on the server, it activates the HTTPS protocol, which secures the connection between the browser and the server.
Commercial SSL certificates are sold by vendors such as GoGetSSL and SSLs.com, at different prices and levels of security, with 128-bit or 256-bit encryption.
Three Types of SSL Certificates
There are three primary types of certificates:
- Domain validation: covers a single domain or subdomain. It is easy to use and cheaper than most.
- Business or organization validation: also covers a single domain or subdomain, but requires a higher level of verification and usually takes one to three days to issue.
- Extended validation: the highest level of verification, usually issued within two to seven days.
2. Get a Free Certificate with Let’s Encrypt
Let’s Encrypt also provides SSL certificates, for free. It is a free, automated and open certificate authority run by the nonprofit Internet Security Research Group (ISRG). If you have shell access to your server, Let’s Encrypt recommends the Certbot client, which obtains the certificate and deploys it for your web server. Without shell access, check whether your hosting provider supports Let’s Encrypt certificates.
3. Install the SSL Certificate on Your Server
The installation is easier with a guide. For a commercial certificate, the following guides can help:
- Install SSL with Apache
- NGINX SSL Certificate Install
- Microsoft IIS SSL Certificate Install
- SSL Install for WHM or cPanel
With Let’s Encrypt, Certbot gives instructions for your web server and operating system:
4. Update Hard-Coded Links to HTTPS
To keep images, scripts and other resources in sync, the hard-coded links in your content must point to HTTPS, rather than a mix of HTTP for some content and HTTPS for the rest.
External resources, plugins and CDNs need manual configuration and testing to make sure everything works correctly.
Backing up the database is an important first step: our guide on how to back up a website explains the options. You can then run the update program from the root of the site over FTP, apply the changes and note each one. The live run shows the result.
HTTPS Migration for WordPress
One of the perks of WordPress is the number of SSL plugins that make the process much easier. If you do not want to change the database yourself, you can use the Really Simple SSL plugin to convert a WordPress website to HTTPS.
5. Update Custom JavaScript and AJAX Libraries
Next, update your custom scripts, third-party scripts included, so the whole site moves to HTTPS without mixed content warnings.
Libraries such as jQuery also need to load over HTTPS.
JitBit’s SSL Check tool scans your site for non-secure content that could cause a mixed content warning.
6. Redirect HTTP to HTTPS with 301 Redirects
A 301 redirect is a permanent redirect that passes ranking signals to the new page. Without it, your SEO rankings could suffer. For a move from HTTP to HTTPS, Google’s guide to site moves recommends server-side permanent redirects, such as 301 or 308, whenever technically possible. Redirects and rankings are what a search engine optimization team in Shanghai watches most closely during this kind of move.
If your site runs on WordPress or Magento, you can set this up through the admin panel. Otherwise, update the .htaccess or web.config file.
The redirect rule should point straight to the HTTPS destination, so you do not need separate rules for HTTPS and the www prefix.
For Nginx, change the server configuration as follows:
server {
    listen 80;
    server_name domain.com www.domain.com;
    return 301 https://domain.com$request_uri;
}
For Apache, add these lines to the .htaccess file:
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule (.*) https://%{HTTP_HOST}%{REQUEST_URI} [R=301,L]
HTTP Strict Transport Security (HSTS) is a web server directive that tells browsers to load resources over HTTPS only. It helps prevent attackers from forcing an insecure version of the site. You can add it to the .htaccess or web.config file.
7. Update the Robots.txt File
Like the .htaccess file, robots.txt needs an update: hard-coded lines and specific blocking rules must reflect the redirect from HTTP to HTTPS.
XML sitemaps, canonical tags, hreflang annotations and the sitemap reference in robots.txt also need to use the HTTPS URLs. Without these updates, Googlebot may not see the content you want it to see. Google’s site move guide also recommends a self-referencing canonical tag on each new URL, and submitting the new sitemap in Search Console.
8. Install the SSL Certificate on Your CDN
A CDN SSL certificate can be installed in three ways: a shared SSL certificate, a custom SSL certificate, or the Let’s Encrypt integration. The steps below use KeyCDN as an example.
Custom SSL has its own KeyCDN guide to free custom SSL for your CDN. This process uses a separate SSL certificate set up as a custom SSL for the CDN, following the KeyCDN guide to setting up custom SSL.
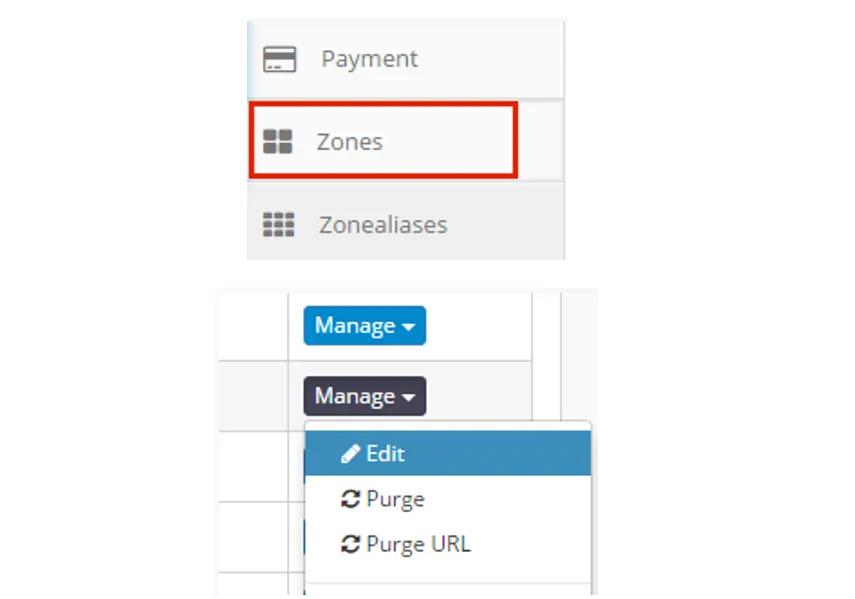
Shared SSL takes several steps. First, click “Zones” in the KeyCDN dashboard, then “Manage” and “Edit”. Next, select “Show advanced features”. Under SSL, enable “Shared” to use the wildcard certificate for the zone: https://*.kxcdn.com. Under “Force SSL”, select “Enable”: this sets up a permanent 301 redirect, which is good for SEO.
For the Let’s Encrypt integration, follow the KeyCDN guide to using Let’s Encrypt.
9. Update the Origin URL on the CDN (and OCSP)
The origin URL also needs an update. On the CDN, go to “Zones” in the KeyCDN dashboard, then “Manage” and “Edit”. For a pull zone, change the origin URL from HTTP to HTTPS, then save.
The Online Certificate Status Protocol (OCSP) is an improvement on the certificate revocation list (CRL). OCSP overcomes the inefficiencies of CRLs: it queries the status of the certificate, and gives a grace period if the certificate expires.
10. Enable HTTP/2 on the CDN
In the KeyCDN dashboard, click “Zones”, “Manage” and then “Edit”. Select “Show advanced features”. Finally, select “Enable” for HTTP/2 and “Save” to update the zone.
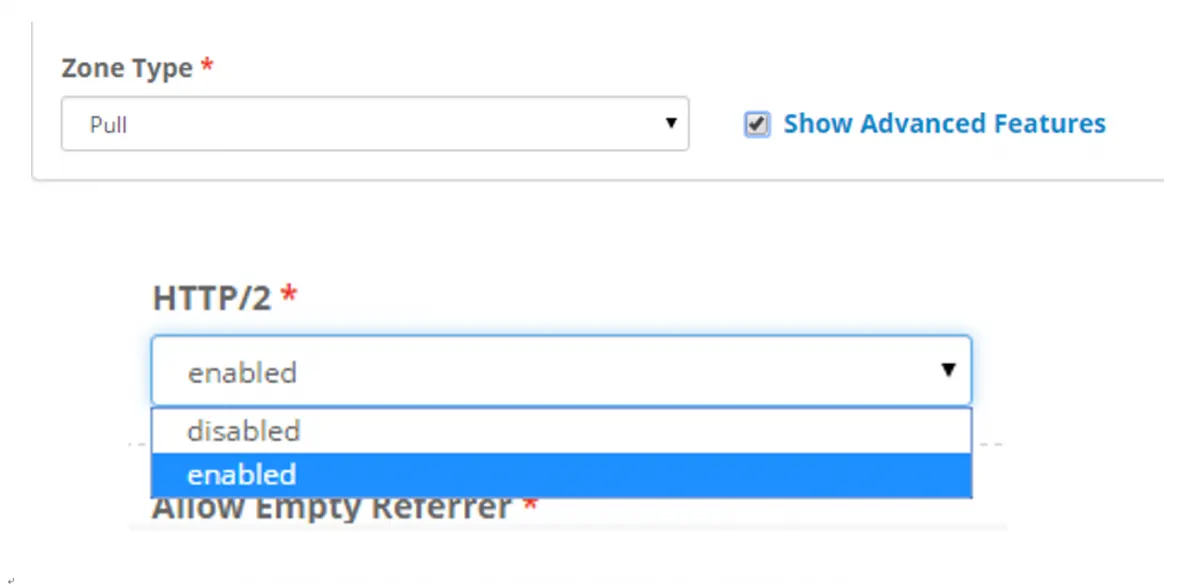
HTTP/2 improves performance and can process multiple requests concurrently. This protocol governs how messages are formatted and transmitted between servers and browsers.
11. Update Google Search Console and Sitemaps
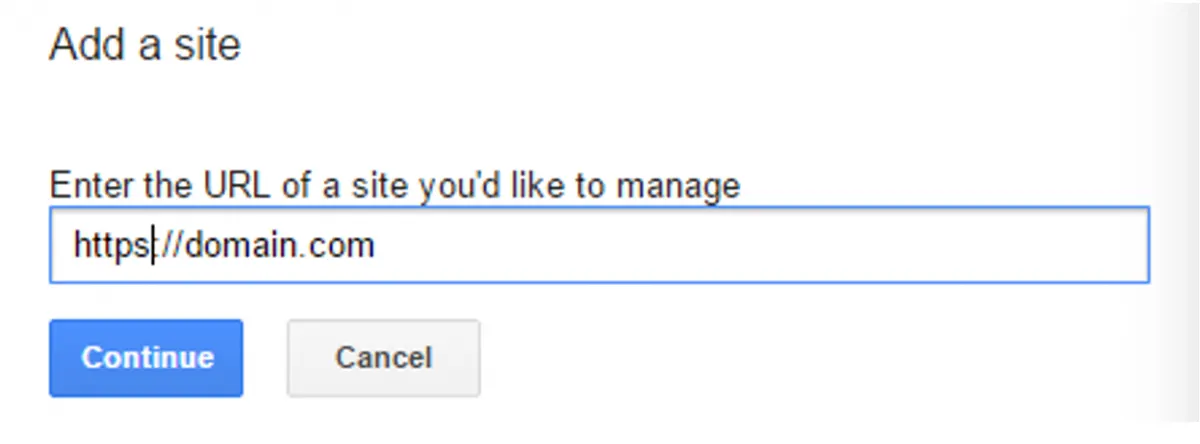
Once HTTPS works, add the HTTPS version of your site as a property in Google Search Console: click “Add property” and follow the steps.
Sitemaps help you debug indexing problems and check which images are indexed. Resubmit the sitemap of the HTTPS version in its Search Console property. Yandex Webmaster Tools uses the same steps, while Bing Webmaster Tools only needs the sitemaps resubmitted.
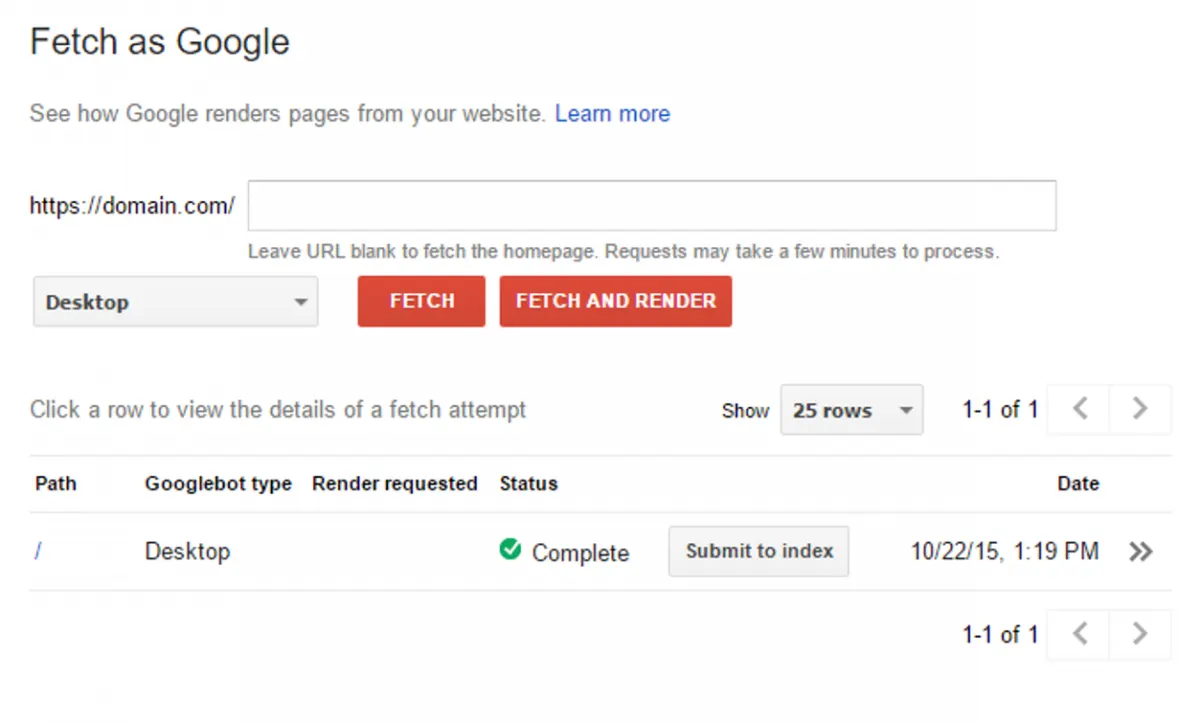
Requesting a crawl can speed things up. When this guide was first written, this step used the Fetch as Google tool: click “Fetch”, then “Submit to index”, and choose to crawl the URL and its direct links. In the current Search Console, use the URL Inspection tool: inspect the HTTPS URL, then click “Request indexing”. There is a daily limit, and a request does not guarantee that the page will be indexed.
12. Resubmit Your Disavow File
If you ever created and submitted a disavow file, for instance after a negative SEO attack, you need to resubmit it for the new HTTPS property. In Google’s Disavow tool, download the original disavow file from the HTTP property.
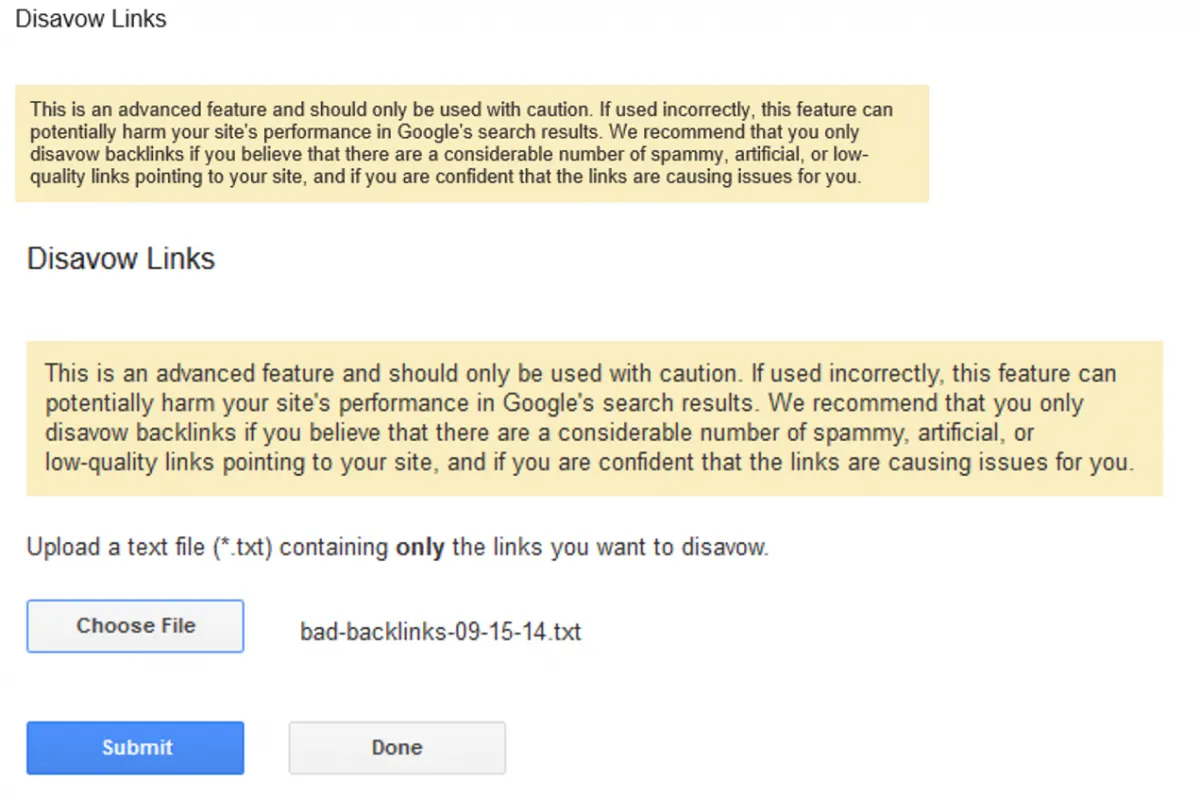
Then open the Disavow tool again for the HTTPS property and upload the file. A confirmation message should appear.
13. Update Your Analytics Settings
The website URL in your analytics account also needs the HTTPS version. When this guide was first written, this meant switching the URL to HTTPS in the view settings and the property settings of Google Analytics. Google Analytics 4 has since replaced Universal Analytics, whose standard properties stopped processing data on July 1, 2023: check that your current analytics setup uses the HTTPS address.
14. Other Updates: Ads, Email and Social Media
The last updates usually involve social media accounts such as Facebook and Twitter, email providers, and applications connected to the website. Use a test environment first, to find bugs and issues. The following updates may be necessary:
- Canonical tags should point to the HTTPS version, including on sites that do not use WordPress.
- Update pay-per-click campaigns, such as Google Ads (formerly AdWords), Facebook ads and Bing Ads.
- Update email marketing software, such as AWeber and Mailchimp.
- Update external links and backlinks as much as possible, and migrate your social share counts.
What Should You Do Next?
By following the steps in this guide, you can convert HTTP to HTTPS in a way that benefits your site: it supports your SEO, improves performance through HTTP/2 and significantly increases security. Test every change before applying it to the live site: you will discover the risks, potential problems and ways to fix them before the website switches to HTTPS.
If you would rather not run the migration yourself, our website maintenance services can take care of your website, from updates to urgent changes.
Frequently Asked Questions
How do I convert HTTP to HTTPS for free?
Use a free certificate from Let’s Encrypt, a nonprofit certificate authority. With shell access to your server, install it with the Certbot client, which gives instructions for your web server and system. Without shell access, check whether your hosting provider supports Let’s Encrypt. Then redirect HTTP to HTTPS with 301 redirects, and update your links, sitemap and Search Console.
Can you switch to HTTPS without an SSL certificate?
No. HTTPS relies on a certificate installed on your server, or on the CDN in front of it. The good news is that a certificate does not have to cost anything: Let’s Encrypt issues free certificates, many hosting providers can manage them for you, and some CDNs, such as KeyCDN, offer a Let’s Encrypt integration.
Does HTTPS improve SEO?
It helps a little. In 2014, Google announced that it would use HTTPS as a ranking signal, describing it at the time as a very lightweight signal that carries less weight than high-quality content. HTTPS also avoids the “Not secure” label that Google announced Chrome would show on all HTTP pages, starting with Chrome 68 in July 2018.